Liquid Hackers Label Blockstream as Delusional, Greedy, and Arrogant While Seeking 10% Bounty
A dispute between Blockstream and parties claiming white-hat hacker status has escalated sharply, with demands for a 10% bounty on roughly $5 billion in secured assets. The conflict highlights security vulnerabilities in the Liquid sidechain and raises questions about bug bounty norms and threat credibility in the digital asset ecosystem.
- Hackers demanded 10% bounty from Blockstream’s own funds after claiming company allocated only $1.5 million to secure $5 billion in assets.
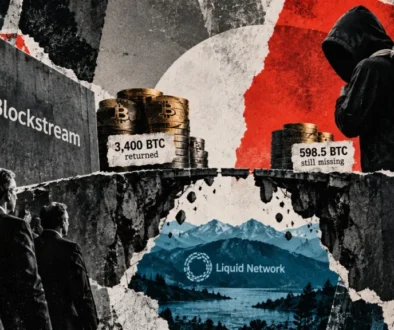
- Roughly 4,000 BTC worth around $320 million was withdrawn from Liquid’s Federation wallet on September 6, with 598 units still held by the hackers.
- Blockstream has kept Liquid paused while addressing security fixes, chain split issues, and preparing coordinated network restart.
- $5B Assets that Blockstream allegedly secured with minimal dedicated funding
- 598 BTC Remaining amount held by hackers after 3,400 BTC was returned
- $320M Value of 4,000 BTC withdrawn on September 6 at the time
- $1.5M Amount allegedly allocated by Blockstream to secure the five billion dollars
Understanding the Liquid Sidechain’s Role and Value
Liquid is a sidechain built on Bitcoin that enables faster transactions and enhanced privacy features for users and institutional participants. The network operates through a federated consensus model where multiple participants maintain bridge nodes that secure the movement of Bitcoin between the main chain and Liquid. This architecture allows Bitcoin to be locked on the main blockchain while an equivalent amount is issued on Liquid, creating a wrapped representation that can be traded with lower latency and fees.
The sidechain has attracted significant institutional interest and daily transaction volumes, making the security of its bridge infrastructure critical to the broader Bitcoin ecosystem. Federation members include major cryptocurrency exchanges and infrastructure providers who collectively ensure that Bitcoin entering the system can be reliably retrieved by users.
The escalating confrontation
The confrontation between Blockstream and the party claiming responsibility for the Liquid bridge breach has intensified as new demands emerge from the actors who withdrew approximately 4,000 BTC from the Federation wallet on September 6. According to messages relayed by Samson Mow, the hackers have characterized Blockstream’s security posture as negligent, pointing to a significant disparity between the value of assets at risk and the resources devoted to protecting them. The group has issued a formal demand for a 10% bounty drawn from company funds, while simultaneously threatening that failure to comply could result in losses of approximately 15% for Liquid users.
Hackers escalate rhetoric against blockstream’s Security response
The messaging from the party holding the stolen funds has grown increasingly confrontational, describing Blockstream’s approach to security as “flagrant neglect” and characterizing the company itself as “delusional, greedy, and arrogant.” The accusations center on what the hackers view as grossly inadequate investment in safeguarding tens of billions of dollars worth of user assets flowing through the Liquid sidechain. This framing represents a departure from the initial posture adopted when the funds were first withdrawn, when the actors described themselves as white-hat researchers and framed the theft as a security demonstration.
The hackers have also indicated they plan to release the private key for decrypting their communications once the bounty dispute concludes.
Industry context and Vulnerability disclosure norms
The cryptocurrency and broader technology sectors have developed established practices for responsible vulnerability disclosure. White-hat security researchers typically report exploits privately to affected organizations, allowing time for fixes before public disclosure. Industry norms generally discourage taking assets as leverage during the disclosure process, though some researchers have historically used modest proof-of-concept withdrawals to demonstrate real-world impact.
The amounts involved in this incident significantly exceed typical bug bounty payouts in the industry, even for critical vulnerabilities. This disparity forms a core part of the hackers’ argument that Blockstream’s standard bounty allocation is insufficient given the scale of assets protected by the vulnerable system.
Blockstream’s measured response and network status
Blockstream and Federation members have maintained the Liquid sidechain in a paused state while implementing additional security fixes and resolving a chain split that emerged during the incident. Users have been advised to refrain from sending Bitcoin to Liquid peg-in addresses until the network restoration is complete. The initial withdrawal on September 6 triggered immediate action from the company, which confirmed that bridge nodes had been patched within a relatively short timeframe.
Following that confirmation, the hackers returned 3,400 BTC to the Federation wallet, representing the majority of the stolen amount, while retaining approximately 598 BTC as what appears to be leverage in negotiations. This staged return suggested an intent to demonstrate the vulnerability without causing permanent loss, consistent with white-hat disclosure practices, though the subsequent demand for compensation has muddied that narrative.
Mow warns Hackers of long-term legal and practical exposure
Samson Mow, former Chief Strategy Officer of Blockstream, has publicly cautioned the group behind the incident that their position may be more precarious than they believe. He highlighted that Blockstream’s willingness to communicate through PGP encryption represented a courtesy that could be withdrawn, and he questioned the strategic wisdom of publicly admitting to the theft and then making financial demands. Mow suggested the actors have left behind evidence that could prove consequential and that attempting to return funds does not necessarily provide an exit from legal or regulatory scrutiny.
His warnings reflect the ambiguous legal territory these incidents occupy. Taking control of assets without authorization, even as a security demonstration, can constitute theft under applicable law regardless of the actor’s intent or subsequent offer to return the funds. Regulatory agencies have increasingly scrutinized such incidents, particularly when public threats are involved.
As a white hat, the road only widens; as a black hat, you’re forever on edge. Dreaming of walking away with assets unscathed is nothing but delusion. Some doors, once opened, can never be closed again.
Samson Mow, Former Blockstream Chief Strategy Officer
Implications for future Vulnerability disclosure
The dispute now hinges on whether Blockstream will engage with the bounty demand and whether the hackers will follow through on threats to escalate damage to the network. The outcome may establish precedent for how exchanges and custodians respond to security disclosures that blur the line between legitimate vulnerability research and theft with conditions.
Should Blockstream accede to demands, it could create incentives for future threat actors to employ similar tactics. Conversely, a firm refusal could potentially encourage the group to make good on threats, creating immediate disruption to users and other Federation participants who depend on Liquid’s operation.
BlockWest is a news publication. Nothing here is investment advice. Read our disclaimer and editorial policy.