Blockstream refuses $50 million bounty demand and risks 600 Bitcoin in Liquid security breach
Blockstream’s refusal to pay a $50 million bounty demand from the Liquid sidechain attacker has triggered a broader debate over how the crypto industry should incentivize partial fund recovery versus deterring future exploits. The standoff tests whether penalizing cooperation discourages future hackers from returning stolen assets or simply shifts the cost of security failures onto users.
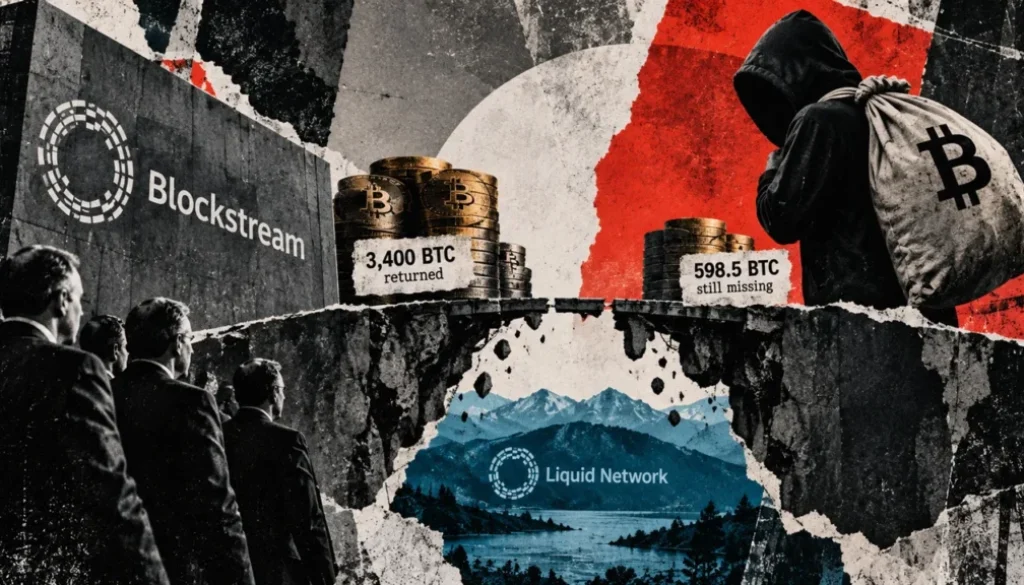
- Attacker demanded 10% bounty on roughly 600 BTC after voluntarily returning 3,400 BTC from September 6 exploit
- Blockstream rejected demand, stating it would pursue remaining funds through law enforcement and forensic specialists instead
- Liquid’s reserve coverage dropped to approximately 85% after attack, leaving core L-BTC-to-BTC peg temporarily impaired
- 600 BTC Remaining stolen funds from Liquid sidechain attack, equivalent to $50 million
- 3,400 BTC Amount voluntarily returned by attacker after Blockstream patched vulnerable nodes
- 85% Reserve coverage of L-BTC after returned Bitcoin was credited back to federation
- Sept. 6 Date of exploit allowing attacker to create 4,000 unbacked L-BTC and withdraw real Bitcoin
Blockstream is standing firm against demands for a substantial ransom payment following a partial recovery from the September 6 exploit that struck its Liquid sidechain. The attacker created approximately 4,000 unbacked L-BTC tokens and withdrew roughly 3,996 real BTC through SideSwap, the main peg-out service on Liquid. After Blockstream patched vulnerable nodes, the attacker voluntarily returned 3,400 BTC but then demanded a 10% bounty paid from Blockstream’s funds, warning that Liquid holders could otherwise face a roughly 15% shortfall on their L-BTC redemptions.
The Liquid sidechain operates as a layer-two solution for Bitcoin, enabling faster transactions and confidential transfers while maintaining a peg to the underlying asset. Users deposit Bitcoin to receive L-BTC tokens backed by a federation of custodians managed by Blockstream and other participants. The security of this peg depends on the integrity of the federation’s reserve management and the cryptographic protocols protecting the sidechain’s consensus mechanism. The September exploit exposed vulnerabilities in that architecture, raising questions about how well-protected Bitcoin-backed sidechains remain against determined attackers.
Blockstream rejects bounty, vows law enforcement pursuit
On September 11, Blockstream announced it would not pay the roughly 600 BTC bounty and instead pursue the remaining funds through law enforcement, cryptocurrency exchanges, service providers, and forensic analysis. The company stated it would not establish a precedent in which developers of open-source software could be forced to pay demands that “far exceeds their economic participation.” Blockstream rejected the attacker’s characterization as a white-hat security researcher and urged the party to return the Bitcoin voluntarily.
The decision has opened a contentious debate within the industry over incentives and moral hazard. Lorenzo Romagnoli, co-founder of USDT0, noted that Blockstream had already achieved an outcome “most hacked crypto protocols could only hope for,” arguing that an attacker linked to state-sponsored or organized criminal groups would have little reason to voluntarily return hundreds of millions in stolen assets.
Blockstream is already in the 1% of the 1% of luckiest hacked protocols on the planet.
Lorenzo Romagnoli, Co-founder, USDT0
Romagnoli warned, however, that refusing a substantial bounty could alter future attackers’ incentive calculations, potentially discouraging cooperation on similar partial recoveries. This tension between establishing precedent and achieving practical recovery outcomes has become a recurring challenge as cryptocurrency platforms face increasingly sophisticated attacks.
SideSwap disputes white-hat status, cites deliberate preparation
SideSwap, which processed the unauthorized withdrawals, disputed the attacker’s characterization as a white-hat researcher. The exchange noted that the party executed 70 similar test transactions before successfully creating the unbacked L-BTC, indicating deliberate preparation rather than accidental discovery. This pattern of behavior suggests the attacker conducted extensive reconnaissance, potentially over weeks, to understand exactly how Liquid’s node infrastructure handled peg-outs and where vulnerabilities existed.
Additionally, the wallet that initiated the attack received funding traced through a cross-chain bridge to Tornado Cash, a mixing service frequently used to obscure asset provenance. SideSwap called the event a “deliberate and prepared attack” and stated it had returned its fees on the transaction while standing with Blockstream’s position. The involvement of Tornado Cash suggests potential premeditation or involvement by actors with experience concealing financial tracks in cryptocurrency transactions.
Samson Mow, former Blockstream chief strategy officer and CEO of Bitcoin company Jan3, also challenged the economics of the bounty demand, arguing that the attacker had based its calculation on Liquid’s total asset value of roughly $5 billion, which includes L-BTC, Tether, and real-world assets issued by different parties and thus does not represent Blockstream’s economic exposure. Under this analysis, Blockstream faced pressure to pay ransom based on a valuation that conflated multiple issuers’ exposure with its own.
Remaining Bitcoin May serve long-term pressure rather than spend
Bitcoin researcher Alex Waltz raised the possibility that the attacker may have no intention of moving the remaining 598.5 BTC through identifiable channels. The wallet is closely watched, and moving the coins through exchanges, custodians, or other regulated services could provide investigators with additional leads. Waltz suggested the attacker now faces a strategic choice: return everything and hope for a generous Blockstream reward, or retain the portion as a means of continued economic pressure even if the coins cannot be readily spent.
The remaining Bitcoin already exerts measurable pressure on Liquid’s operations. As of September 10, 4,205 L-BTC remained in circulation while the federation reserve held 3,597 BTC, resulting in approximately 85% reserve coverage. Blockstream Chief Executive Adam Back said the L-BTC-to-BTC peg will ultimately achieve one-for-one coverage and urged holders not to sell at a discount, but the company has not yet disclosed how it will finance the shortfall if the attacker refuses to return the funds.
The economic pressure on Liquid holders is real and immediate. Any user holding L-BTC faces potential losses if they attempt to redeem their tokens before Blockstream resolves the reserve gap. This dynamic creates secondary pressure on Blockstream to settle with the attacker, even as the company maintains its public stance of non-negotiation. Markets often price in tail risks, and L-BTC trading discounts would reflect the probability that holders may not recover full Bitcoin value.
Liquid has resumed producing blocks and SideSwap markets have reopened, but peg-ins and peg-outs remain disabled while the federation completes a security review. SideSwap announced it will keep its peg service offline until the federation introduces a new security architecture and will disclose those changes before resuming operations. Until either the coins return or the reserve gap is filled through other means, Liquid’s core promise of converting L-BTC back into Bitcoin at parity remains suspended.
Blockstream’s next move depends on tracing the remaining BTC and identifying whoever controls the wallet. The company has not detailed whether it will seek to finance the roughly 600-BTC gap from its own balance sheet or recover it through legal and forensic channels, nor has it specified when full L-BTC redemptions will resume on Liquid’s network. The outcome of this standoff could influence how other blockchain projects respond to future exploits and ransom demands.
BlockWest is a news publication. Nothing here is investment advice. Read our disclaimer and editorial policy.