Ethereum privacy initiative faces processing challenges as solo validation demands approximately twice the expected gas fees
Ethereum’s push toward privacy features is running headlong into the network’s computational limits, with cryptographic proof verification costs nearly doubling proposed gas allowances. The resolution of this tension will determine whether privacy can become a native Ethereum capability or remain confined to centralized relay services.
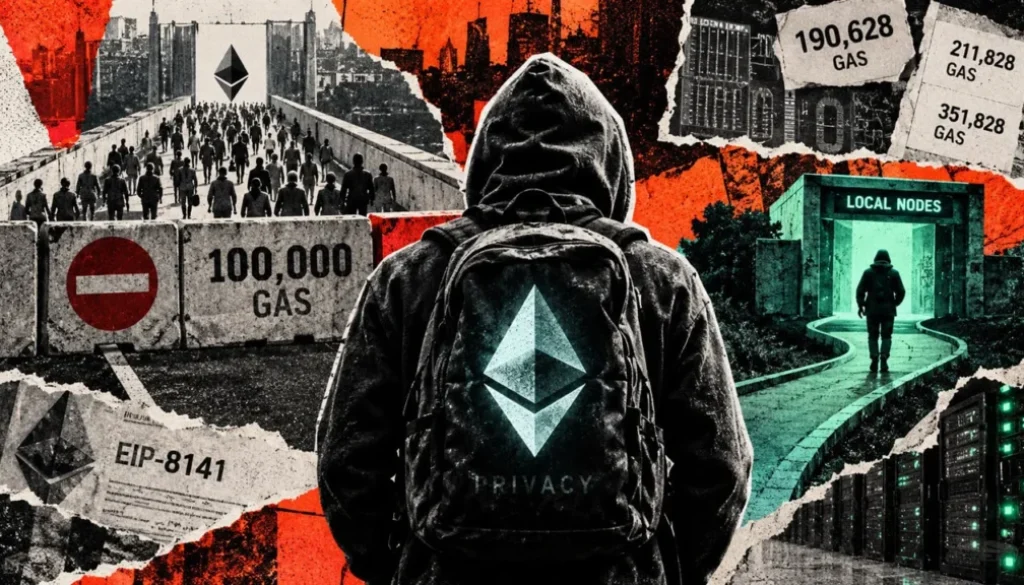
- A single optimized Groth16 proof verifier requires 190,628 gas, nearly double the 100,000-gas limit proposed in EIP-8141
- The cryptographic pairing check alone consumes 181,000 gas, already approaching the entire proposed validation budget
- EIP-8141 proposes a tiered model allowing higher-capacity nodes to accept privacy transactions locally without network-wide propagation
- 190,628 Gas required for single optimized proof verifier versus 100,000-gas limit
- 181,000 Gas consumed by cryptographic pairing check alone
- 351,828 Gas needed for eight-note spend transaction versus baseline allowance
- 250,000 Gas minimum recommended by benchmark author for typical optimized transactions
Ethereum’s privacy roadmap faces a fundamental technical impasse as the computational cost of verifying zero-knowledge proofs far exceeds the validation budget the network currently permits. A September 2 benchmark by researcher mmjahanara found that a single optimized Groth16 proof verifier demands 190,628 gas, compared to the 100,000-gas cap outlined in the September 5 EIP-8141 proposal. Groth16, one of the industry’s most widely adopted zero-knowledge proof systems, is valued for its compact proofs and efficient verification, making it attractive for privacy protocols seeking minimal on-chain computational footprint.
Yet the mathematics of elliptic curve operations required for proof verification consume far more gas than traditional transaction validation, creating a direct conflict with Ethereum’s design philosophy. This technical friction has emerged as developers attempt to move privacy functionality from the margins of the ecosystem into Ethereum’s core protocol layer.
Proof verification nearly doubles the proposed Gas limit
The EIP-8141 draft establishes a 100,000-gas cap for signature verification and transaction execution during initial validation, a constraint designed to control node resource consumption, mitigate denial-of-service vulnerabilities, and ensure that any computer can run a full validating node without specialized hardware. The cryptographic pairing check that forms the core of Groth16 verification alone requires 181,000 gas, already consuming nearly double the entire proposed allowance.
This gap reflects a deeper incompatibility: zero-knowledge proof verification inherently requires intensive elliptic curve operations that modern processors handle less efficiently than simple arithmetic operations. The pairing operations involve multiple field multiplications and additions across complex mathematical structures, each consuming substantial computational resources that translate directly into gas costs.
Current privacy protocols including Tornado Cash and RAILGUN mitigate this problem through relayers that submit transactions on behalf of users, insulating privacy users from direct on-chain interaction but introducing trust assumptions and operational centralization risks. If these protocols were to replace off-chain relayers with public transaction submission, they would require nodes to accept and propagate proof-verification processes that directly collide with current gas constraints. This relayer dependency represents a significant architectural compromise in the pursuit of practical privacy.
EIP-8141 proposes a tiered validation model for higher-capacity nodes
Contributor AnkushinDaniil’s September 5 proposal seeks to establish the existing validation maximum as a minimum floor that all nodes must support, while allowing higher-capacity nodes to locally accept more demanding transactions without mandating network-wide propagation. This tiered approach reflects recognition that Ethereum’s monolithic validation model may require adjustment to accommodate advanced cryptographic operations.
Such a model introduces significant complexity into Ethereum’s previously uniform validation rules. By allowing different nodes to enforce different thresholds, the proposal creates potential pathways for transaction propagation unevenness across the network: transactions accepted by high-capacity nodes might face rejection elsewhere, complicating wallet and application development while potentially fragmenting the network into tiered classes of validators based on hardware capacity.
The benchmark author mmjahanara recommends allocating at least 250,000 gas for typical optimized transactions, though formal adoption has not yet established this threshold. Even this higher allowance would remain insufficient for eight-note transactions, which demand 351,828 gas combined. This persistent gap suggests that incremental gas limit increases alone may prove insufficient to solve the underlying verification cost problem.
Network propagation and mempool rules present additional obstacles
Increasing gas allowances alone would not eliminate all technical constraints on Ethereum’s privacy implementation.
EIP-8250, a companion proposal, restricts each sender to one pending public-mempool transaction at a time, a limitation that poses difficulties for privacy designs sharing addresses. More broadly, network propagation differs from block validity: EIP-8141 permits transactions outside its public rules to exist in local or private mempools, but this does not guarantee network-wide acceptance. This distinction between local validation and network propagation introduces complexity to Ethereum’s transaction relay architecture, historically built on relatively uniform rules across nodes. Private mempools and relay mechanisms already operate at the margin of the Ethereum ecosystem, used by sophisticated traders and specialized services, but expanding them as a primary privacy mechanism would represent a structural shift in the network’s design.
Ethereum researchers have explored alternative pathways including trusted execution environments, rollup-based solutions, and alternative consensus mechanisms to sidestep gas constraints entirely. Each approach carries different security and decentralization implications. Layer 2 solutions such as Arbitrum and Optimism already host privacy protocols that avoid mainnet gas constraints through separate validation and proof systems.
EIP-8369, a separate informational proposal, outlines potential future rules for enforcing transaction inclusion through custom or direct submission methods, though implementation would require a binding protocol extension. For privacy designs studied in the benchmark to receive guaranteed public access, the network would need to accommodate their proof costs across all participating nodes, a question the Ethereum community has not yet resolved.
Without such accommodation, privacy transactions may remain dependent on relay services and alternative submission mechanisms rather than achieving first-class status on the public blockchain. The outcome will shape not only Ethereum’s privacy capabilities but establish precedent for how the network handles future features requiring substantial computational overhead. The Ethereum community’s decisions on EIP-8141, EIP-8250, and related proposals in the coming months are expected to clarify the path forward and determine whether privacy can become a native feature or remains confined to centralized workarounds.
BlockWest is a news publication. Nothing here is investment advice. Read our disclaimer and editorial policy.