Cryptocurrency wallet developers must notify regulators within one day of discovering security vulnerabilities being used in attacks
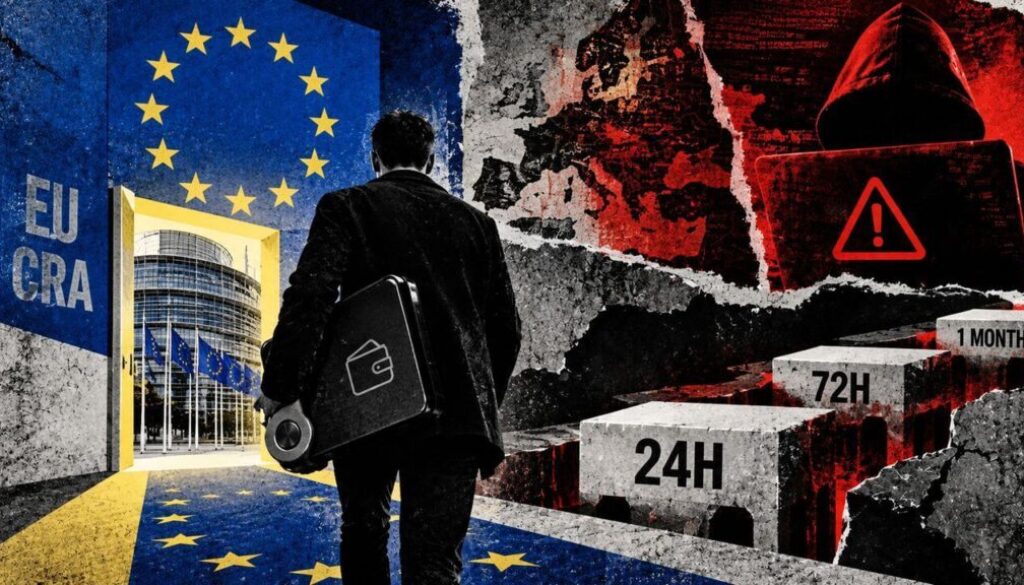
The EU’s Cyber Resilience Act now requires wallet makers to report exploited flaws to regulators within 24 hours, a requirement now in effect for both new and existing products sold in Europe. This marks a significant tightening of disclosure obligations for crypto infrastructure providers operating in the region.
- Wallet manufacturers must file an early warning within 24 hours of discovering an actively exploited vulnerability or severe security incident.
- A fuller notification is due within 72 hours, followed by a final report within 14 days for vulnerabilities or one month for severe incidents.
- The rule applies to both hardware wallets and downloadable wallet software made available on the EU market with network connectivity.
- 24 hours Maximum time to file initial early warning after discovering exploited vulnerability or incident
- 72 hours Deadline for fuller notification with detailed information about product and remediation steps
- Sept. 11, 2026 Effective date when rapid reporting requirement took effect under EU Cyber Resilience Act
- Dec. 11, 2027 Date when open-source software stewards’ reporting duties and broader product-security requirements begin
Starting Sept. 11, 2026, wallet creators whose products meet the European Union’s product test must alert cyber authorities within 24 hours of learning that a vulnerability is being actively exploited or that a severe security incident has occurred. The requirement flows from the EU’s Cyber Resilience Act, a horizontal product law that applies to hardware and software with digital elements distributed on the EU market, provided their intended or reasonably foreseeable use includes a direct or indirect data connection to a device or network.
Both commercial hardware wallets and downloadable wallet applications can fall within the scope. The EU has not issued a definitive list of covered brands or services, leaving wallet makers to self-assess whether their products trigger the regulatory obligations. This ambiguity has prompted industry participants to seek clarification from national regulators and to develop conservative compliance strategies.
The Cyber Resilience Act represents part of the European Union’s broader push to strengthen digital security across consumer-facing products and infrastructure. By establishing mandatory vulnerability disclosure requirements, EU policymakers aim to reduce the window of time during which attackers can exploit security flaws and harm users. The wallet industry, which handles significant user assets and personal data, was singled out as a priority sector under this regulatory framework.
Three escalating reporting deadlines shape manufacturer obligations
Manufacturers face a three-stage filing process through the Single Reporting Platform operated by ENISA, the EU’s cybersecurity agency. The first step is an early warning due without undue delay and no later than 24 hours after discovering the vulnerability or incident, indicating which member states received the affected product and whether unlawful or malicious activity is suspected.
A second, more complete notification must follow within 72 hours unless relevant information was already provided in the early warning. For actively exploited vulnerabilities, this fuller filing adds general details about the product, the exploit itself and the vulnerability, plus any corrective or mitigating measures already in place. For severe incidents, it describes the nature of the incident, provides an initial assessment and shares available mitigation information.
The final deadline diverges by incident type: vulnerability reports are due no later than 14 days after a corrective or mitigating measure becomes available, while severe-incident reports are due one month after the 72-hour notification, as specified in the regulation. This staged approach gives regulators time to assess the severity of disclosed issues while holding manufacturers accountable for rapid initial notification.
Existing Wallets covered, open-source software gains limited exemption
The reporting requirement applies to products placed on the EU market before Dec. 11, 2027, meaning wallet makers cannot avoid the new obligations by pointing to existing product lines launched before the Cyber Resilience Act took broader effect. This ensures that currently distributed wallets face the accelerated disclosure timeline immediately.
Open-source software receives limited relief under the regulatory framework. The European Commission’s guidance clarifies that commercially supplied free and open-source products can trigger manufacturer obligations, though non-monetized software supplied by its developer should not count as commercial activity. Individual contributors are not treated as manufacturers for software outside their responsibility.
Open-source software stewards, a separate legal category, do not face these reporting duties until Dec. 11, 2027, when the CRA’s main product-security requirements take effect. This staged implementation recognizes the distinct governance structures and resource constraints of the open-source ecosystem while maintaining security expectations over time.
Manufacturers must alert users and coordinate with national teams
Beyond regulatory filing, manufacturers must inform affected users and, where appropriate, all users when corrective action is needed, including steps users themselves can take. This dual notification requirement ensures that regulators and end users receive timely information about emerging threats and remediation options.
The Single Reporting Platform routes notifications to ENISA and the designated coordinating Computer Security Incident Response Team for each member state, then supports distribution to other relevant national teams. This centralized infrastructure aims to prevent information fragmentation while enabling coordinated responses across EU jurisdictions.
The Sept. 11 effective date launches only the rapid reporting regime; the CRA’s broader requirements for secure design and product-lifecycle management do not take effect until Dec. 11, 2027. Wallet makers should audit their current compliance posture and establish notification procedures now, as the first test of these obligations will come when the next significant hardware or software vulnerability surfaces in a product offered to EU users. Industry observers expect the initial reporting season to reveal implementation challenges and opportunities for regulatory clarification.
BlockWest is a news publication. Nothing here is investment advice. Read our disclaimer and editorial policy.