
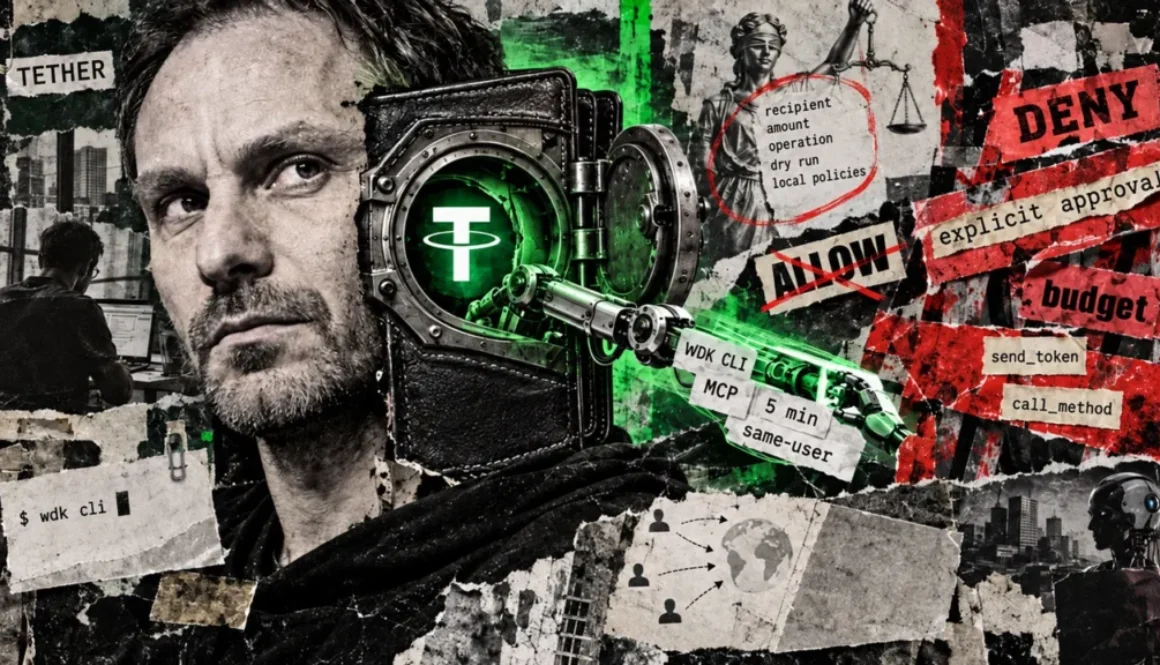
Paolo Ardoino advocates for AI agents to possess Tether while developers bear responsibility for excessive costs
Tether’s Wallet Development Kit offers builders flexible tools to let AI agents control cryptocurrency, but the responsibility for setting spending limits falls entirely on developers rather than being enforced by the protocol itself. For enterprises and users deploying autonomous agents with financial authority, this design choice creates both opportunity and risk depending on how carefully developers implement transaction controls.
- Tether’s WDK CLI establishes a five-minute default session after wallet unlock, during which any process owned by the same operating-system user can request transactions without re-entering the passphrase.
- The SDK provides optional ALLOW and DENY rules for transaction policies, but developers must independently track cumulative spending, recipient approvals, and concurrent requests to enforce budget limits.
- Three separate tools, the CLI, SDK, and MCP Toolkit, offer different security models; a developer’s choice of integration determines which safeguards apply to AI agent spending.
- 5 min Default session duration after wallet unlock before automatic re-locking
- Nov. 11 Date Tether announced the Wallet Development Kit to the public
Tether CEO Paolo Ardoino has outlined a vision of financial autonomy spanning people, machines, and AI agents, with human wallet owners retaining custody of private keys. The Wallet Development Kit, announced on November 11, 2024, aims to enable that architecture by providing developers with multiple ways to build assistants capable of moving money. But Tether’s own documentation reveals a fundamental tension: the protocol layer does not enforce spending limits, leaving developers responsible for designing and implementing controls that ensure agents operate within intended boundaries.
The emergence of AI agent control over cryptocurrency reflects a broader shift in how blockchain applications are being architected. As autonomous systems become more prevalent in financial operations, the need for secure delegation mechanisms has grown correspondingly. Unlike traditional banking systems where institutional controls are embedded in the infrastructure itself, blockchain-based solutions often place security responsibilities on application developers and their design decisions.
Session Unlock Grants Access Without Per-Transaction Approval
Tether’s September 3 explanation of WDK CLI, a local command-line wallet built with the Kit, describes a practical model for agent access. When a wallet owner unlocks it on macOS or Linux, the system starts a five-minute timed session. During that window, any other process running as the same operating-system user can request the daemon holding the unlocked wallet to sign transactions without re-entering the passphrase.
The architecture preserves custody because the seed remains encrypted at rest, but it eliminates the need for fresh human approval of each payment once a session begins.
Tether frames this as an accepted trade-off for hot-wallet operation, comparable to other self-custody tools. Users can shorten the default five-minute session, manually re-unlock to reset the timer, or disable automatic expiry entirely by setting the lifetime to zero. This flexibility reflects recognition that different deployment scenarios require different security postures; a developer testing locally may accept looser controls, while production systems handling significant assets demand stricter safeguards.
However, a short session window does not by itself establish an amount limit or require the user to make a fresh decision about each recipient. That distinction matters for any developer building an assistant that can move money, and it represents a critical gap between authentication (proving the user is who they claim) and authorization (confirming they intend this particular action).
SDK Transaction Policies Require Developer Implementation
Developers building applications can access the WDK SDK directly, which includes configurable ALLOW and DENY rules that can block transaction requests before they reach the wallet or blockchain. These policies can specify approved recipients and amount conditions, and they execute locally rather than on-chain, reducing latency and gas costs compared to on-chain enforcement.
But the documentation explicitly states they are not a complete sandbox: certain internal module calls and raw account references remain outside their interception. This partial coverage means developers cannot assume the policy engine will catch every possible spending path.
More consequentially, the SDK does not automatically handle critical functions that cumulative budget enforcement demands. Developers must independently maintain recipient lists, fetch token prices, decode contract-call data, and track cumulative spending over time periods such as daily budgets. A product that promises a ceiling on daily agent spending must record every prior transaction and handle simultaneous requests consistently, or the limit becomes meaningless. That accounting sits with the application, not the wallet, requiring developers to implement distributed ledger and concurrency logic that has historically been a source of bugs and vulnerabilities.
The implication is that a spending limit is only as reliable as the application logic surrounding it.
Three Tools, Three Security Models, One Developer Choice
Tether’s documentation divides the WDK into three distinct interfaces, each with different control points. The CLI serves local operator workflows with its session-based access model. The SDK sits inside applications and offers optional transaction policies developers can implement. The separate MCP Toolkit, documented as beta.1, provides another approach where Tether says its built-in write tools obtain explicit user approval before broadcasting transactions.
That separation gives developers options as they move from experimentation to production systems handling user funds. The customizable MCP Toolkit also lets builders add their own operations, but then they must decide what authority to grant each added tool. Tether’s own framing distinguishes these approaches from the CLI’s recommended workflow of previewing a payment, showing its details, obtaining confirmation, and then executing. But the daemon does not require proof that those earlier steps occurred; an otherwise valid execution request can still broadcast from an unlocked wallet through another permitted path.
The divergence between intended and actual security posture has become a recurring issue in cryptocurrency applications. When multiple integration paths exist, users and auditors must understand not just what safeguards are theoretically available, but which ones actually apply to their specific deployment.
For a user deploying an AI agent with financial authority, the meaningful security promise is specific: what can this assistant spend, where can it send funds, and what ends its authority? That answer depends entirely on which tool a developer chooses, how they configure its rules, and whether the surrounding application logic actually enforces the limits they claim to have set. Developers now face the responsibility of making delegated agent authority match the spending restrictions users believe they have established.