
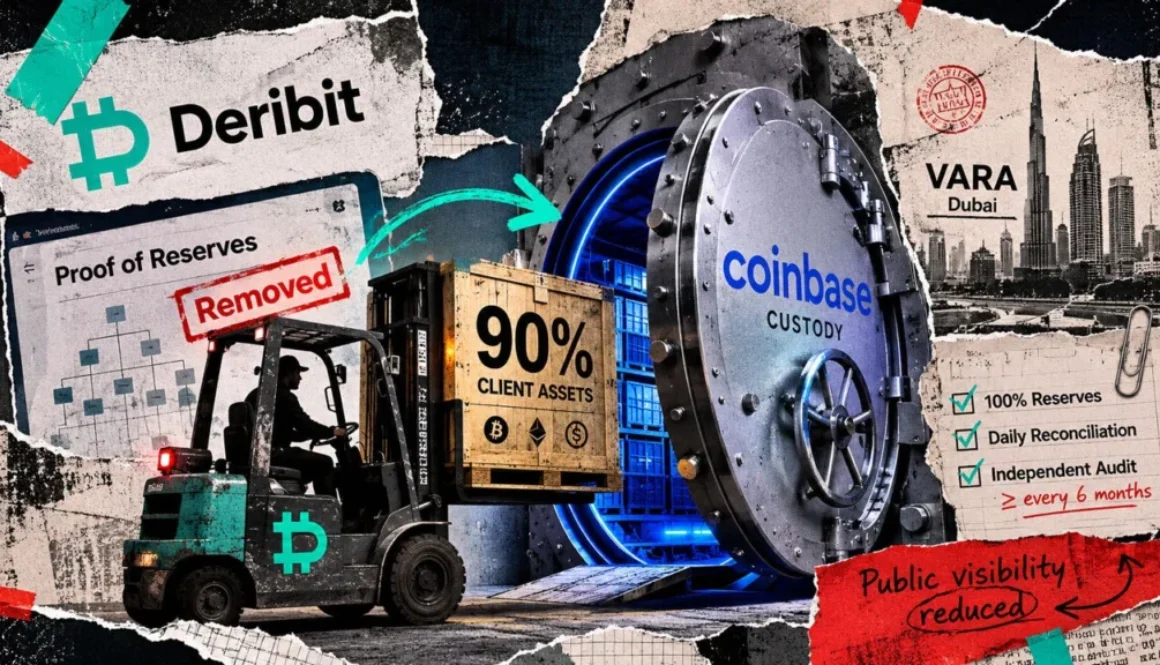
Deribit transfers majority of client funds to Coinbase before discontinuing regular asset verification audits
Deribit’s discontinuation of its public Proof of Reserves page marks a significant reduction in customer-accessible transparency, even as regulatory oversight mechanisms remain in place under Dubai’s Virtual Assets Regulatory Authority. The move follows the derivatives exchange’s August 2025 acquisition by Coinbase and the transfer of approximately 90% of client assets into Coinbase custody.
- Deribit will discontinue its public Proof of Reserves page on September 1, 2025, ending daily transparency verification for customers.
- Approximately 90% of client assets have been transferred to Coinbase custody arrangements since the acquisition closed in August 2025.
- Regulatory audit and reserve requirements under Dubai’s VARA remain mandatory, but customers lose real-time self-directed verification capabilities.
- 90% of client assets transferred to Coinbase custody since acquisition
- Sept 1 date when public Proof of Reserves page will be discontinued
- 100% reserve-to-liability ratio required by Dubai’s VARA regulations
- 6 months maximum interval between required VARA reserve audits
Deribit announced the removal of its daily Proof of Reserves transparency tool as part of a broader infrastructure overhaul tied to its integration with Coinbase, which acquired the derivatives exchange in August 2025. The public page, which operated using a privacy-preserving binary Merkle tree structure with daily snapshots, allowed individual customers to verify their account balances and independently cross-check the exchange’s total liabilities against its published wallet holdings. Any member of the public could also sum the file’s total liabilities and compare that figure to Deribit’s disclosed wallet balances. The move represents a shift from continuous public transparency to on-demand reporting, reflecting broader industry trends as custody models evolve.
Proof of Reserves systems have become standard across cryptocurrency exchanges following major collapse events in 2022, particularly the failures of FTX and related platforms that exposed serious gaps in customer asset protection and exchange solvency verification. These mechanisms allow customers to verify that exchanges maintain sufficient assets to cover all customer balances, addressing fundamental concerns about operational integrity and asset segregation. The discontinuation of such tools has drawn attention from industry observers and regulatory advocates who emphasize the importance of customer-accessible verification mechanisms.
The Merkle Tree System Deribit Is Discontinuing
Deribit’s existing Proof of Reserves system assigned each client a unique proof identifier to locate hashed entries representing their balances within a daily snapshot structure. The methodology allowed customers to independently verify their balances without requiring access to the exchange’s full customer database, protecting individual privacy while enabling transparency at the aggregate level. The Merkle tree approach is widely regarded as one of the more sophisticated privacy-preserving verification methods available to exchanges seeking to balance transparency with confidentiality concerns.
The system had inherent limitations even before removal. According to Deribit’s stated approach, assets held with third-party custodians were already excluded from the Proof of Reserves reporting because they fell outside Deribit’s direct control, with Copper ClearLoop cited as an example. This exclusion means that as the portion of customer assets held in third-party custody increased, the utility of Deribit’s Proof of Reserves mechanism correspondingly declined, covering only the subset of assets under direct exchange control.
Industry practitioners have noted that the shift toward custodial arrangements reflects genuine operational advantages and risk management benefits. Third-party custody providers like Coinbase maintain specialized security infrastructure, insurance coverage, and regulatory oversight that many exchanges lack independently. However, this structural evolution creates new transparency challenges, as customers must ultimately trust multiple parties across increasingly complex custody chains rather than conducting direct verification against a single exchange’s published wallets.
Regulatory Requirements That Remain in Force
Deribit operates as Deribit FZE under Dubai’s Virtual Assets Regulatory Authority, which maintains distinct reserve and audit requirements entirely separate from the exchange’s operational decisions. VARA regulations require covered virtual asset service providers to maintain reserves equal to 100% of client liabilities on a one-to-one basis in the same asset, reconcile them daily, and obtain independent third-party reserve audits at least every six months. Deribit’s regulatory filings reference both annual and twice-yearly Proof of Reserves audits, exceeding VARA’s minimum audit frequency of once every six months.
Additional VARA mandates require that covered firms submit wallet addresses monthly and provide statements demonstrating compliance with financial requirements on a quarterly basis. VARA’s active service-provider register lists Deribit FZE as an exchange and broker-dealer. The regulatory oversight framework operates independently of Deribit’s decision to remove the public page, and any violations would constitute regulatory infractions rather than merely customer-initiated verification gaps.
Dubai’s regulatory regime has positioned itself as a comprehensive framework for virtual asset service providers, with specific emphasis on reserve adequacy and customer asset protection. The VARA’s audit requirements and reserve mandates create an independent verification mechanism theoretically capable of detecting insolvency or asset deficiencies, though regulatory audits typically occur on defined schedules rather than continuously, creating potential gaps in real-time verification.
Unclear Custody Arrangements With Coinbase
Deribit’s disclosures name Coinbase at the brand level regarding the migrated assets but do not identify the specific Coinbase legal entity holding the transferred client funds.
A separate VARA service-provider list names Coinbase for custody and self-custody technology services without specifying which entity is involved. The ambiguity matters because different Coinbase legal entities may operate under different regulatory regimes, insurance arrangements, and segregation protocols. VARA membership terms allow assets to be held directly or through third-party custodians while requiring segregation from company assets and preservation of clients’ legal title. The regulatory framework does not prevent third-party custody arrangements, but requires proper disclosure and controls that should clarify the specific custodial entity and its regulatory status.
The lack of specific entity identification raises questions about regulatory supervision clarity and the verifiability of segregation between Deribit’s operational assets and customer funds across multiple jurisdictions and corporate structures.
After September 1, clients and counterparties may request audited financial statements and other due-diligence materials on demand, but Deribit has not committed to providing a replacement public dashboard or continued client-level Merkle verification. This means customers will lose the ability to perform real-time, self-directed verification of their holdings independent of regulatory audits, returning to an information asymmetry model where verification depends primarily on regulatory enforcement rather than continuous public accountability mechanisms.